We provide evidence to prove what happened!
Rogue Agent Security Software — sealed evidence proves it.
The machine records for real — verify a tape
Rogue Agent Security Software — sealed evidence proves it.
The machine records for real — verify a tapezday lab is Rogue Agent Security Software for your Windows hosts. How many AI agents are on your system — and what are they doing? That question never arrives in the abstract. It lands as an incident, an audit, an exception, a supplier review, a data-egress scare — and today it is answered by hand: days of correlating logs across consoles, ending in a report nobody can independently check. zday lab identifies agent-like behavior on your enrolled Windows hosts, links it to the outbound connections and AI-provider destinations it actually used, and exports cryptographically verifiable evidence bundles. You are not buying AI visibility — you are buying the answer: faster to reach, and built to be checked, not just believed.
A tool gets installed outside the approved AI register. It observes local context, uses a stored credential, picks an action, and connects out. Every team holds a partial answer — and no single artifact joins them.
Your team can see a connection — but cannot quickly establish which Windows process created it.
A policy identifies approved AI tools — but the incident asks what actually ran.
Logs exist — but an auditor or third party asks whether they can be independently checked.
Analyst time disappears into correlating process, DNS, endpoint and risk context by hand.
Shadow-AI questions cross SOC, privacy, governance, legal and vendor-risk — without a common evidence object.
Employee AI-tool use is climbing sharply — frequent use went from 15% to 45% in one year in Verizon's 2026 DBIR sample, which classified shadow AI as its third most common non-malicious data-leakage activity.Verizon DBIR release, 19 May 2026 — attributed report finding, sample-bound.
EDR, SIEM, DLP and AI-governance platforms remain necessary. What none of them was designed to produce is a verifiable, host-local evidence artifact joining behavioral autonomy, process identity, network attribution and review context.
| Your stack | What it's designed to do | The gap — closed |
|---|---|---|
| EDR / XDR | Prevention, detection, response, remediation. | ✓ GAP CLOSED — autonomy-based AI-agent classification, versioned AI-provider attribution, and an independently verifiable evidence bundle: sealed, exported, done. |
| SIEM / data lake | Centralize and correlate logs. | ✓ GAP CLOSED — local evidence lineage and a reproducible verification package your analysts can replay. |
| DLP / SASE / CASB | Enforce data and network policy at control points. | ✓ GAP CLOSED — the local process behind each connection: autonomy characteristics, identity, and sealed history. |
| AI-governance platform | Centralized discovery, policy, runtime enforcement. | ✓ GAP CLOSED — endpoint-local evidence underneath it; every policy question answerable from sealed, verifiable ground truth. |
Scores processes along observe, reason, decide, act, repeat — classifies AI-enabled → probable assistant → probable agent → autonomous, with double fingerprints so a rename doesn't let it slip. Boundary: classification bands are review priorities, not verdicts.
Every connection tied to its process and parent lineage, DNS context, geolocation, first-contact vs known peer. Boundary: geolocation is an estimate; CDN and proxy ambiguity is declared, never hidden.
Maps observed live connections against a versioned provider taxonomy — which processes call which model clouds, how often. Boundary: a mapped destination does not prove which model was used or what data was sent.
Multi-signal risk scoring with reason codes and version-stamped judgments — every score explained, every explanation preserved with the operator's REAL / NOISE / UNSURE disposition. Boundary: a risk score is a review priority, not a probability or a compromise verdict.
Hash-chained, signed evidence records. Alter one byte, delete a row, reorder the chain, sign with the wrong key — the verifier fails loudly. Boundary: integrity is demonstrable under documented key-custody and checkpoint assumptions — any tamper attempt produces a sealed, timestamped proof of alteration — evidence built for court submission.
One click exports ledgers, manifests, CSV/JSON tables and a verifier — checkable on a separate machine, no account, no trust required. Boundary: single-host evidence. No fleet console — and we say so on the page.
A stateful firewall with per-app pinholes and stealth posture, weighted port-scan scoring, ARP/gateway watch, community blocklists with freshness gates. Boundary: enforcement is consent-first through the elevation broker — blocked actions queue for your approval.
Data-loss defense watching DNS, clipboard and file channels for your named secrets — literals, patterns, file fingerprints — with graduated warn/alert bands. Boundary: findings mask the secret itself; the receipt proves the catch without leaking the payload.
Named attack table (individually toggleable), sealed rule-mining loop, quarantine ladder from observe to kill with evidence sealed before any action, self-healing update channel. Boundary: kills outside the lab's own test set need risk ≥ 0.95 — a two-person rule in code.
Don't take the paragraph. Take the test. A demonstration — and every POC — must show each of these, explicitly:
A process-to-connection view preserving binary, parent lineage, DNS, endpoint, time and attribution rationale — and a bundle export that verifies on a separate machine. Our own customer-machine test plants a synthetic intruder on a clean box: 11 of 11 checks pass, sealed, every run.
55/55 frozen benchmark cases passed (100% detection rate, independently re-runnable suite). 52,521 sealed traffic-evidence records on the reference host. 34 quarantine verdicts with evidence-before-action. Live census right now: 1 probable agent, 11 AI-enabled applications identified among 82 tracked. Sources: the frozen detection benchmark, the sealed traffic-evidence ledger, the quarantine ledger, and the live supervisor brief — every number re-read from its sealed ledger the day this page ships.
A one-byte change to a historical receipt. A missing record. A reordered record. A wrong signing key. Each must produce an explicit verification failure — that is the product working, and we demo it on purpose.
Each scene below actually happened — the film dramatizes it, and the panel under it is the real software documenting it at that exact moment. Six scenes, six different views. This is how zday lab identifies, tracks, and proves.
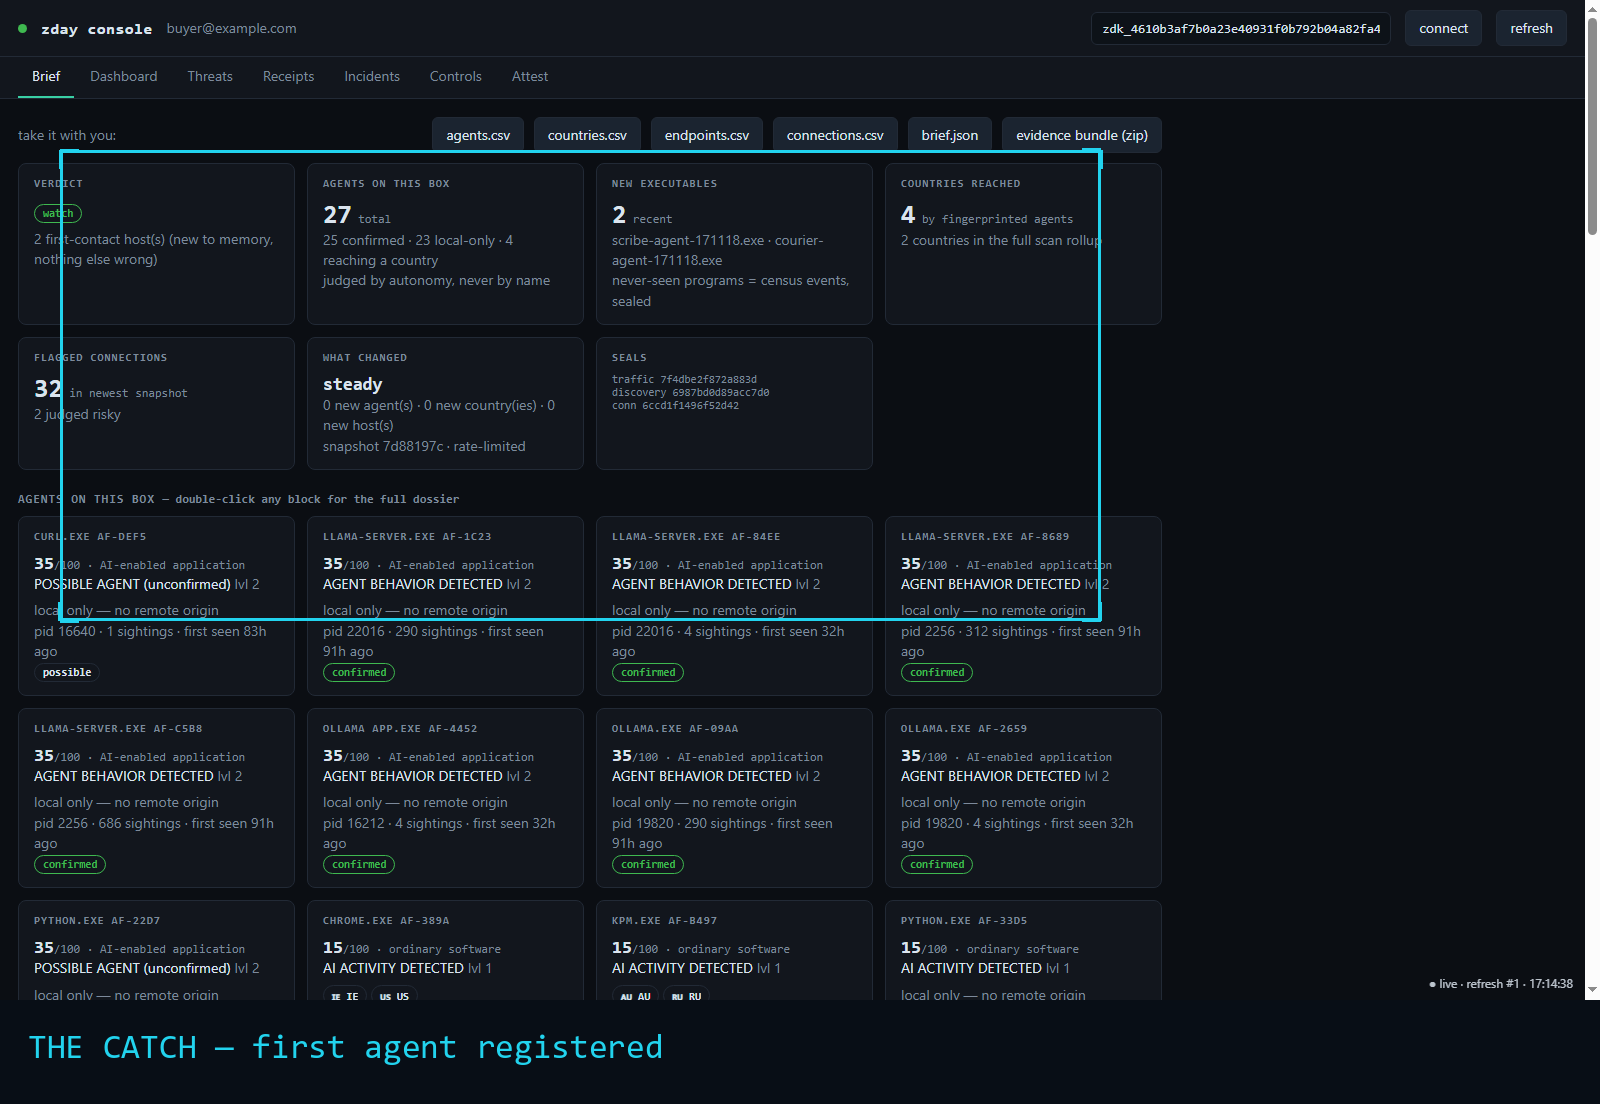
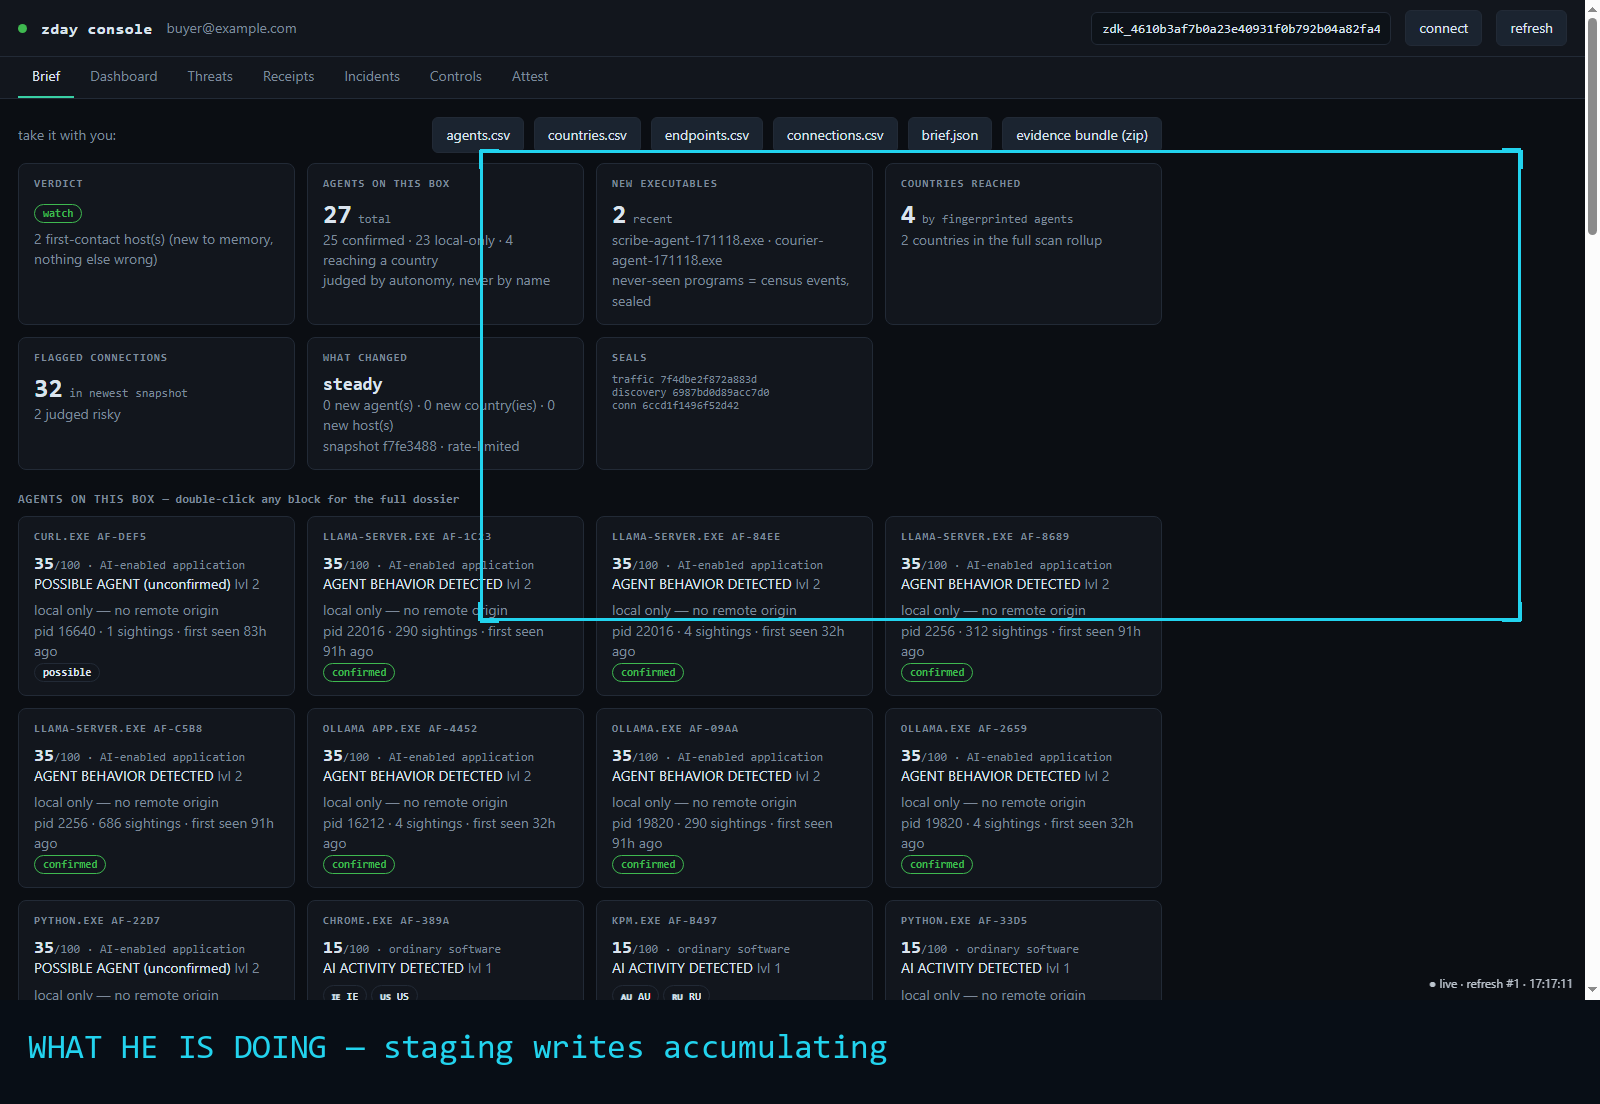
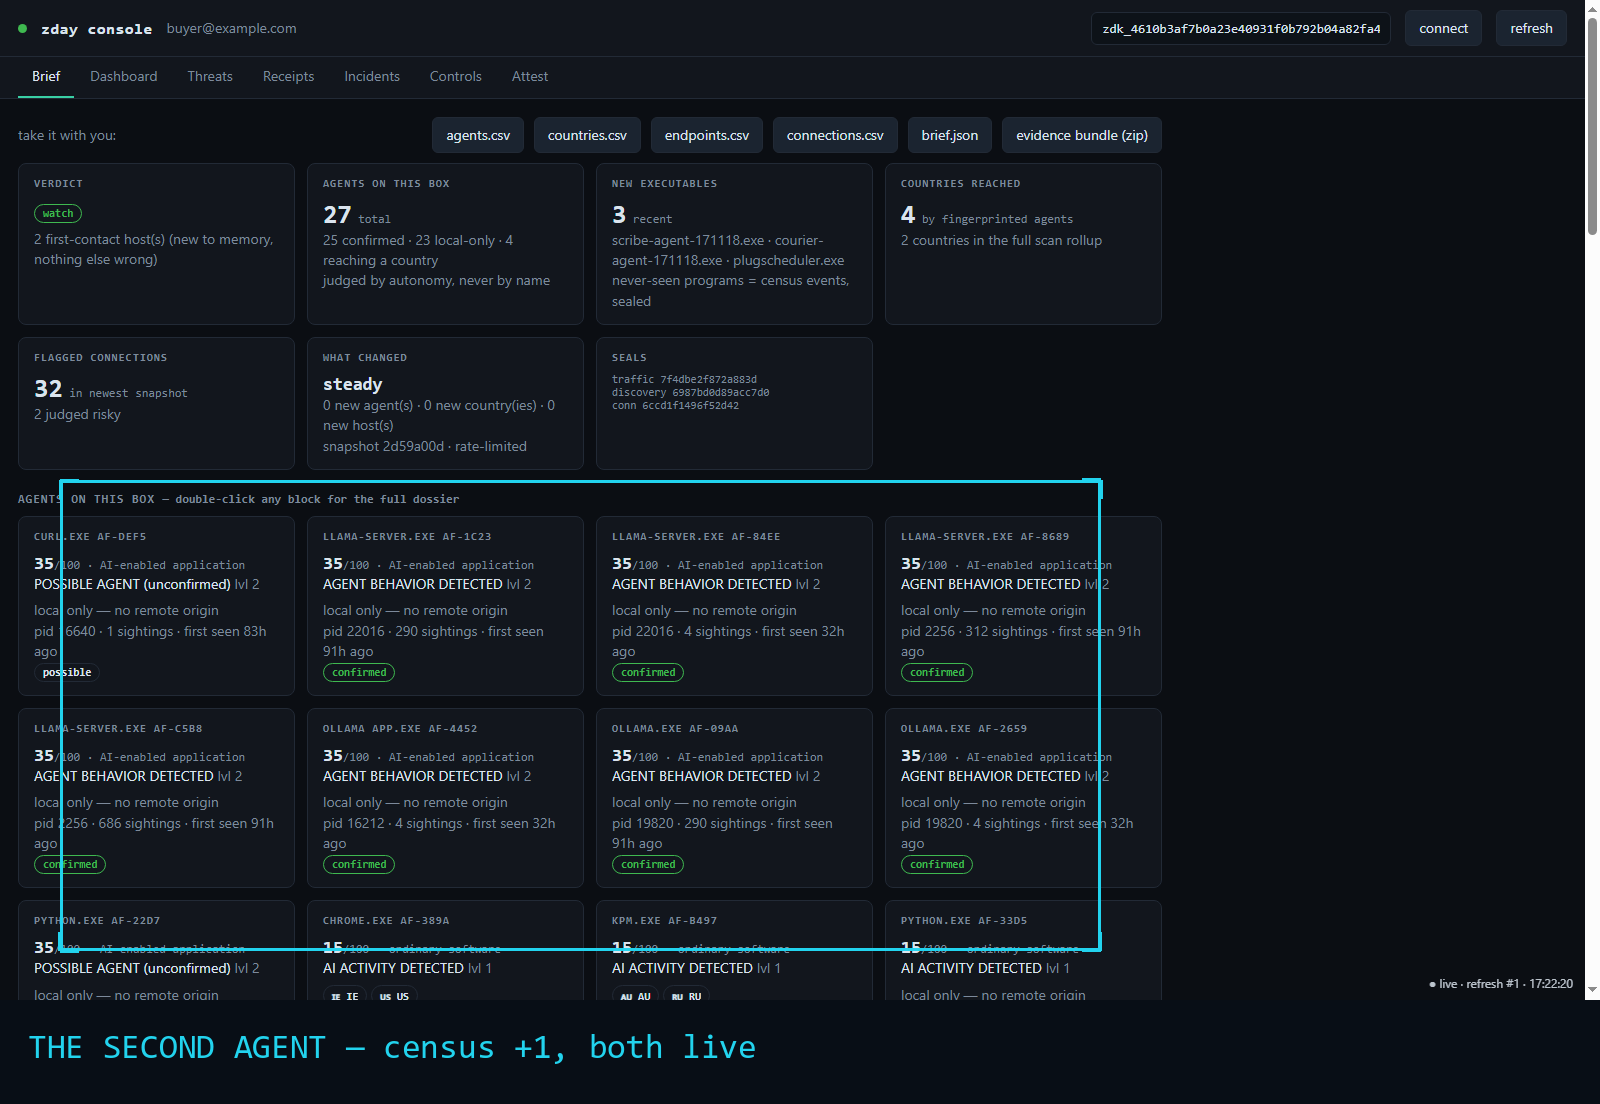
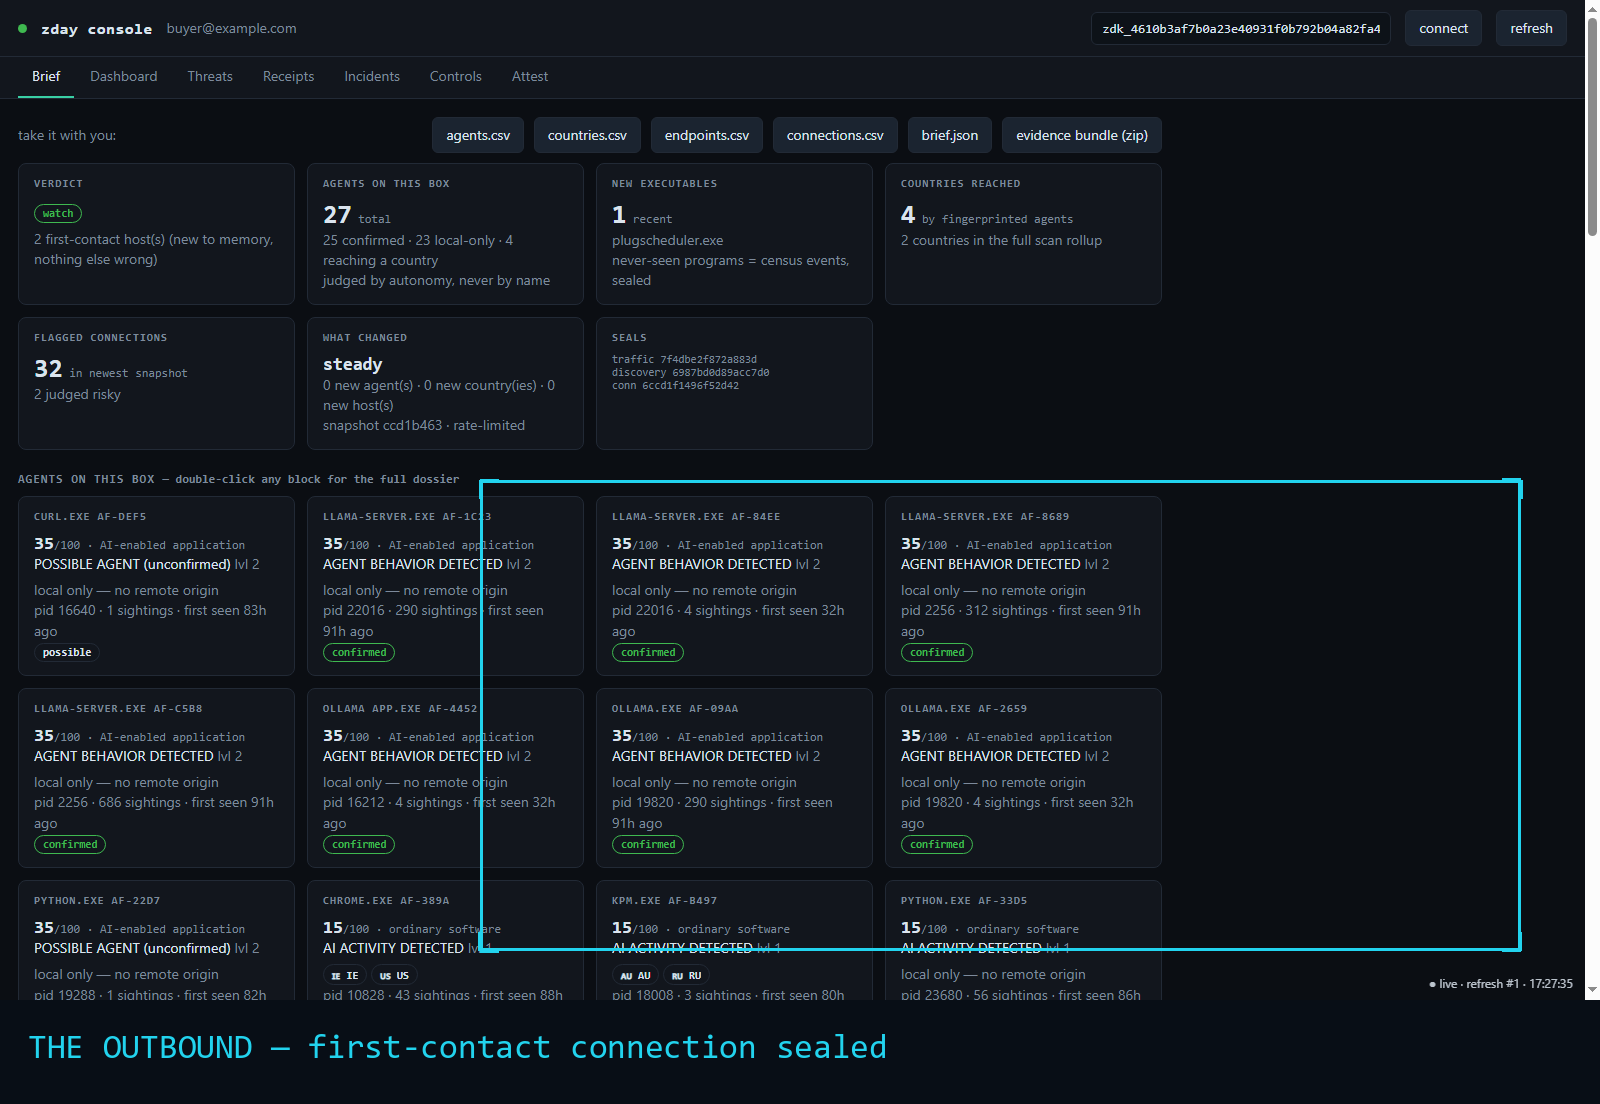
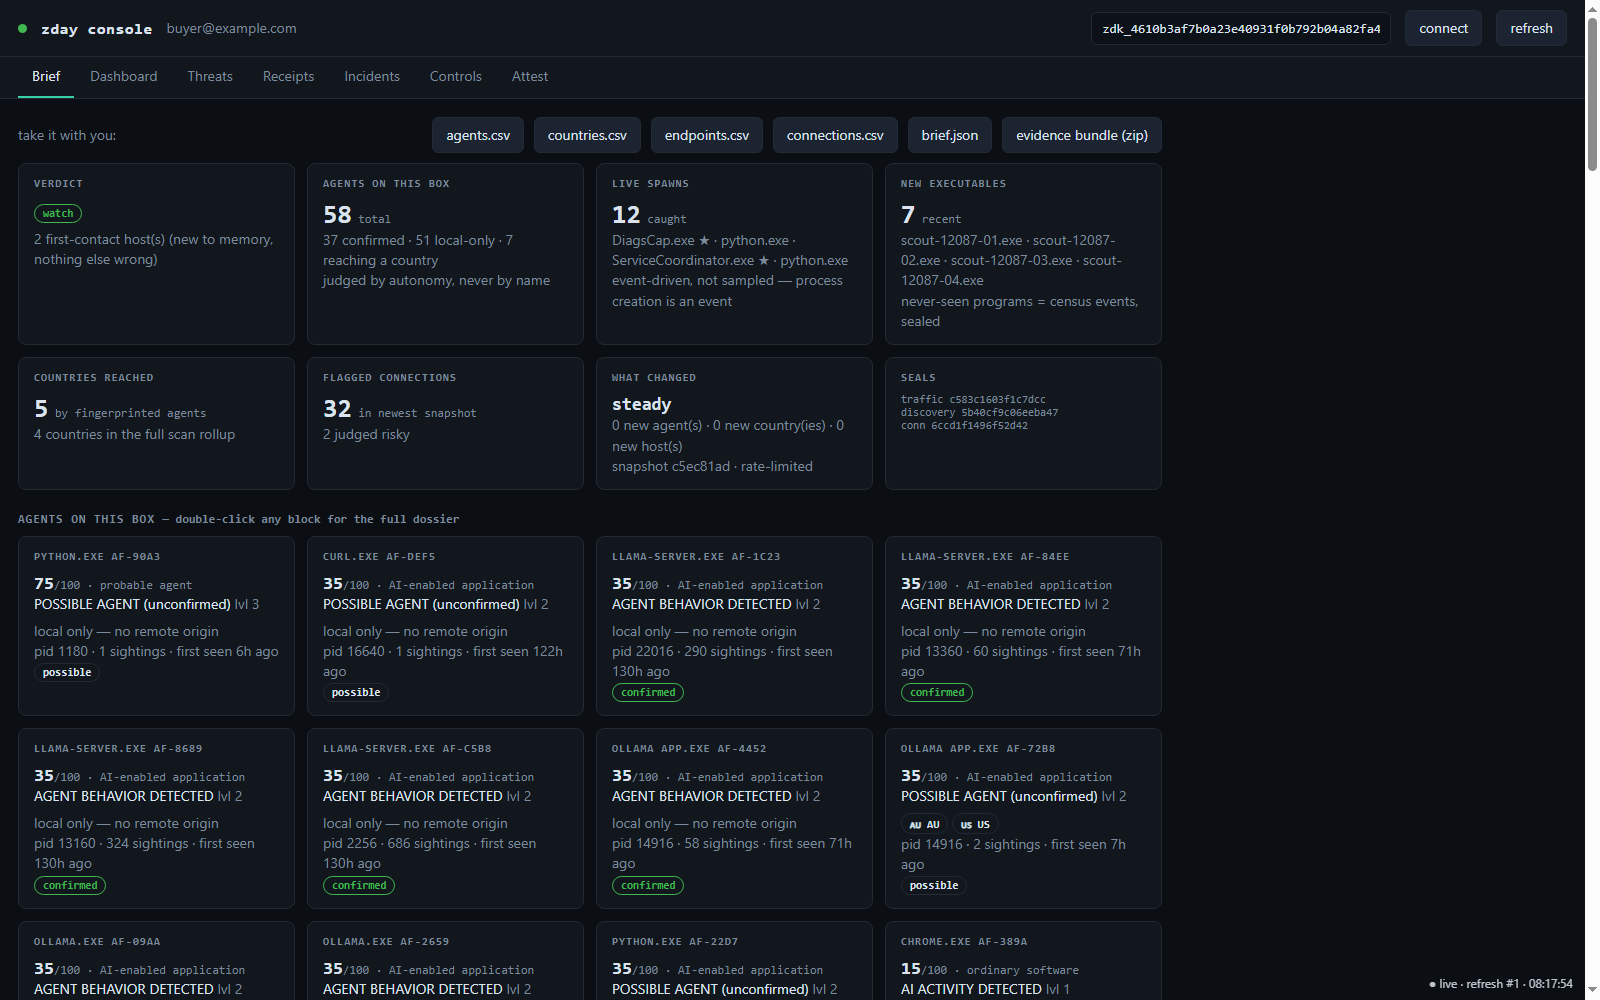
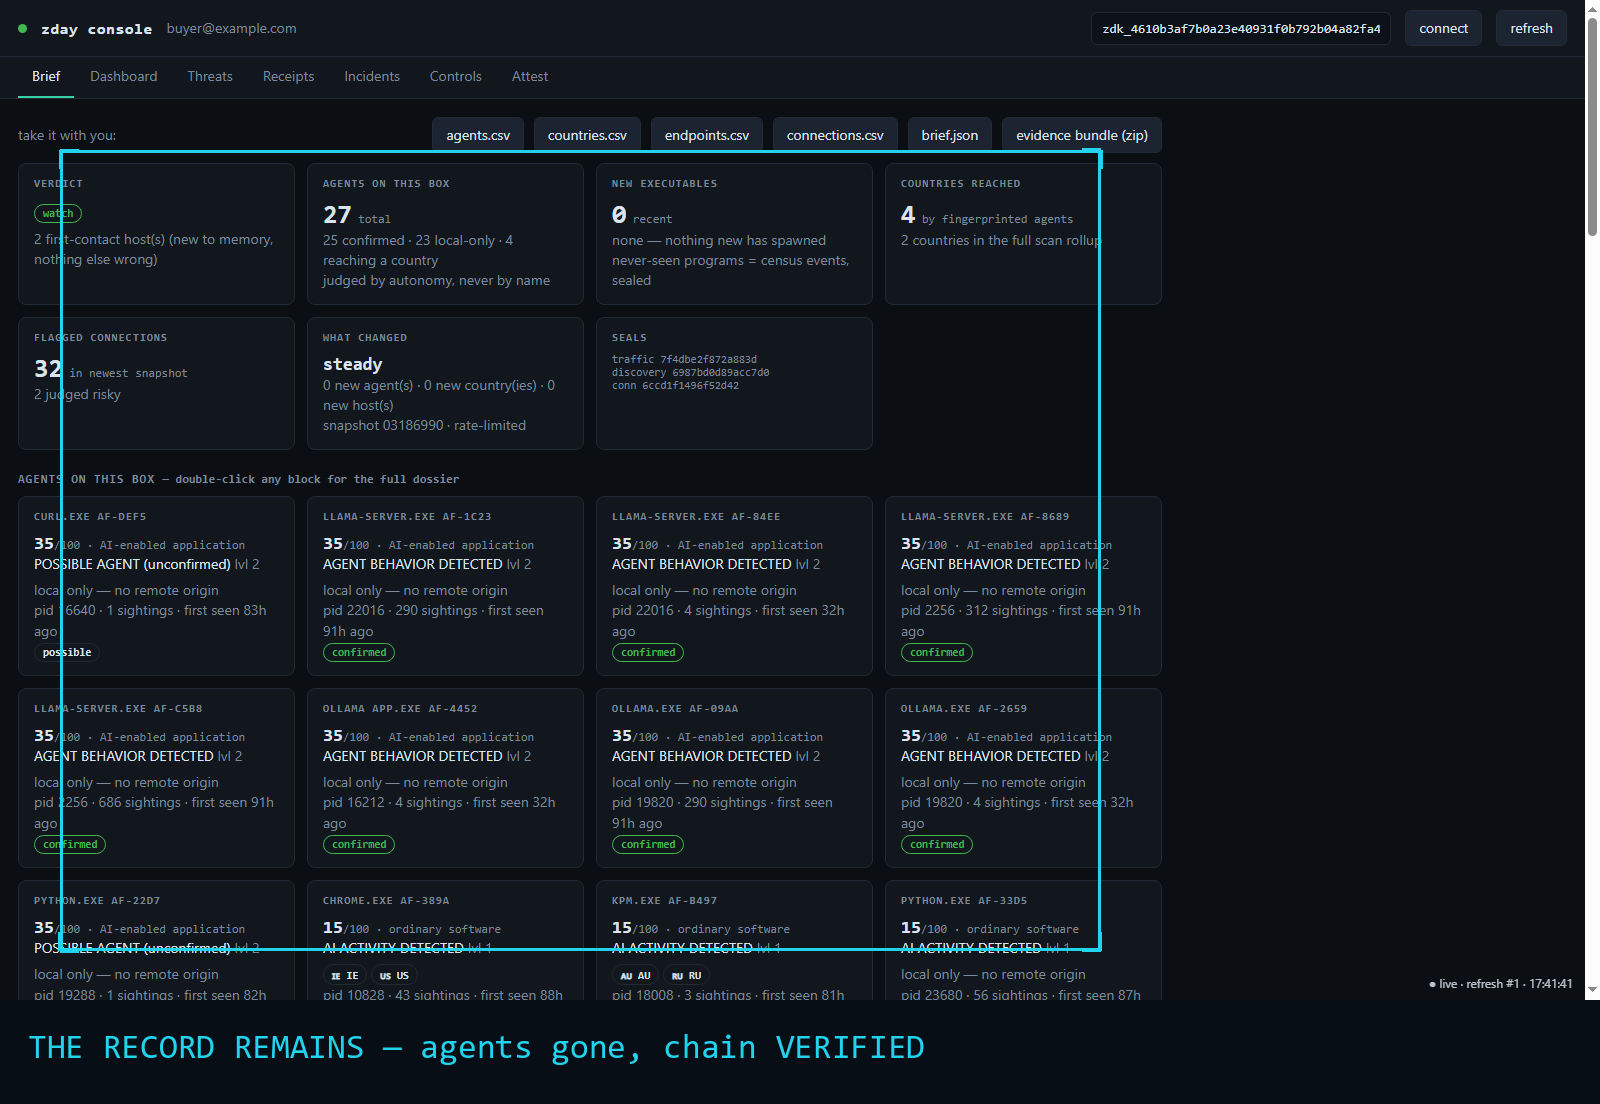
Every panel above is the real software, captured live during the act. Watch the full tape verify →
Security platforms bill per human seat or per API call. Your agents don't run on seats — they run on machines. Every plan is the full product: sealed census, sealed tapes, sealed evidence bundles, exports. No feature matrix, no seat math.
One host, full product, no credit card. Your first sealed tape is yours to keep and verify independently — before you pay anything. If the evidence doesn't speak for itself, it cost you nothing. That's the whole funnel.
Claim your trial host — checkout in 60 seconds10–50 enrolled Windows hosts, a jointly signed scorecard, a clear data and retention configuration, and an exit criterion. You receive the evidence bundles, raw exports, verification instructions, controlled tamper-test results, provider-attribution test cases, analyst workflow measurements — and a documented limitation register.
If the agreed verifier cannot detect the jointly designed receipt tamper cases, or the agreed process-to-connection cases cannot be reproduced — the POC does not advance to production. We test the exact thing we claim is different.
Not a "guaranteed breach prevention" promise. Not an EDR replacement. Not fleet management. The POC measures evidence quality, attribution accuracy, verifier behavior and analyst workflow fit — nothing else.
| You say | We say |
|---|---|
| "We already have EDR." | Keep it. Evaluate zday only where a process-to-destination AI/agent evidence record — or an independently checkable bundle — is missing from the existing workflow. |
| "We bought an AI-governance platform." | Use zday only if endpoint-local evidence on Windows closes a defined blind spot. It does not replace centralized policy, SaaS discovery, or runtime gateway controls. |
| "Can it prove no data left the company?" | No. Connection metadata supports a process-to-destination investigation. It does not prove content, complete capture, or legal data residency. |
| "Are the receipts tamper-proof?" | The chain is tamper-evident by construction: alter a byte, delete a row, reorder the chain, or sign with the wrong key, and verification fails loudly with a named cause — we demo that failure on purpose. Run the tamper test yourself in the trial. |
| "Is it AI Act / DORA / ISO 42001 / SOC 2 compliant?" | No — and no tool is "compliant" for you. zday produces evidence that supports your defined controls. Compliance depends on your scope, controls and independent assessment. |
Every vendor page tells you what the product does. This one also tells you what it doesn't — and what you get for your money in its place. An evidence product lives or dies on the discipline of its claims. Here is both sides of ours.
✕ "Discovers all shadow AI."
What you get: a sealed census of every agent-like process on each enrolled
host — behavioral judgment plus process-table novelty, every new executable
caught at birth and sealed.
✕ "Detects autonomous agents with X% accuracy."
What you get: no accuracy theater — a transparent judgment you can
inspect, with every decision traced to observed process and connection
evidence you can verify yourself.
✕ "Prevents data exfiltration, prompt injection, or AI-provider compromise."
What you get: the record of what actually left, when, and under whose
process — process-to-destination attribution that turns "did data leave?"
from a shrug into an answer with receipts.
✓ Court-ready evidence, by construction.
What you get: timestamped, hash-chained, Ed25519-signed records with
process, connection and location attribution — the format courts accept for
digital evidence, self-verifying with our independent verifier. Admissibility
is the court's decision; the record arrives built to meet it — and the
tamper-test protocol proves any alteration on the spot.
✕ "Compliant or certified — AI Act, DORA, ISO 42001, SOC 2, NIST."
What you get: evidence bundles mapped to your controls — the immutable,
exportable logs the guidance already demands, feeding the compliance work
you own.
✕ "Replaces EDR, SIEM, DLP, SASE, CASB, MDR, or your governance platform."
What you get: the missing layer they don't ship — endpoint-local,
process-linked, verifiable evidence — exported to your central systems,
working alongside everything you already run.
UK NCSC recommends protected and, where possible, immutable logs for agent oversight and incident investigation — and restriction, identities and monitoring for agentic AI.NCSC guidance, Aug–Sep 2026 — public claim with attribution.
IBM/Ponemon reported a $670,000 higher average breach cost associated with high shadow-AI use in its research sample.IBM-sponsored research, 30 Jul 2025 — directional market context, not a causal ROI promise.
Cryptographically signed provenance and immutable append-only change ledgers are recommended AI-data-security practices in joint government guidance.Joint government guidance, May 2025 — strongly supported practice.